Capstone · Cybersecurity ML
Hybrid ML Intrusion Detection
A real-time hybrid intrusion detection system that runs an ensemble of ML models over network traffic and maps every alert to MITRE ATT&CK.
The challenge.
Signature-based tools miss novel attacks, and SOC analysts drown in alerts with no context about what an attacker is actually doing. The job was a detector that catches unknown behaviour and tells the analyst what it means.
The approach.
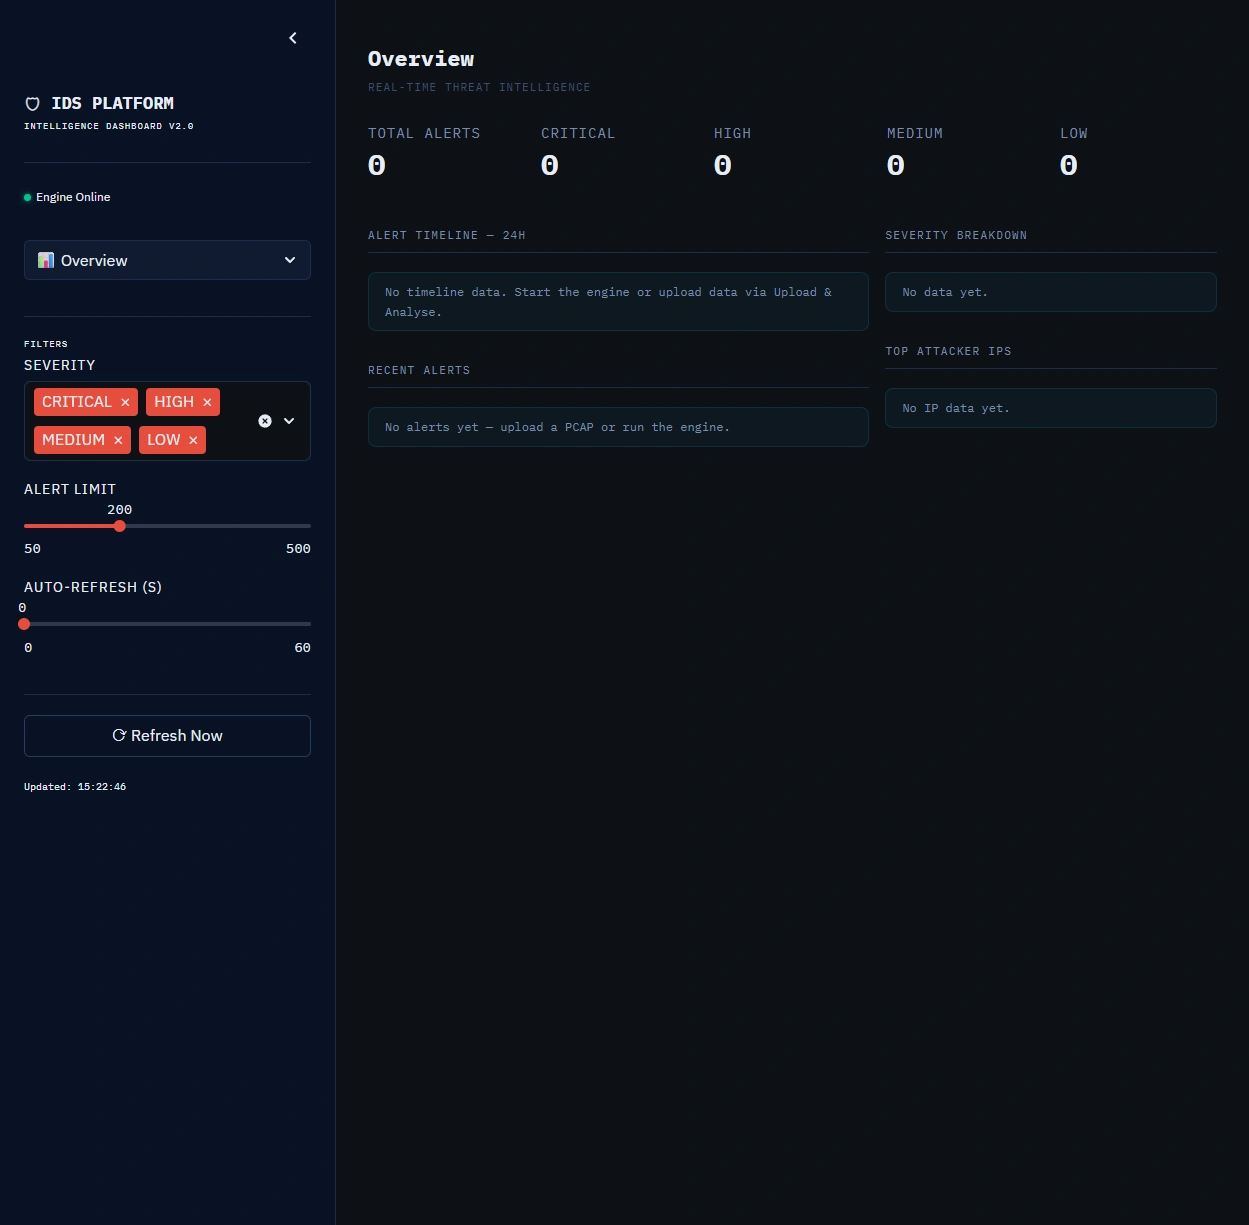
A hybrid NIDS and HIDS that runs an Isolation Forest, Random Forest and Autoencoder ensemble over CICIDS2017 traffic, with a real-time Streamlit dashboard. Live packet capture runs through Scapy; every alert is mapped to its MITRE ATT&CK technique so the analyst sees intent, not just a flag.
Engineering decisions.
-
Ensemble of three complementary models: Isolation Forest for unsupervised anomalies, Random Forest for known classes, Autoencoder for reconstruction-error outliers.
-
Every detection is mapped to a MITRE ATT&CK technique, so an alert reads as attacker intent rather than a bare label.
-
Live packet capture and feature extraction with Scapy feeding the models in real time.
-
Containerised with Docker and shipped as an interactive Streamlit dashboard anyone can run.
The outcome.
Detects DDoS, brute force, port scans, web attacks, infiltration and botnet activity across the CICIDS2017 categories. The ATT&CK mapping turns each alert from a raw flag into a triage decision in seconds. Deployed live on Hugging Face Spaces with full source on GitHub.