Threat Intelligence
ThreatLens
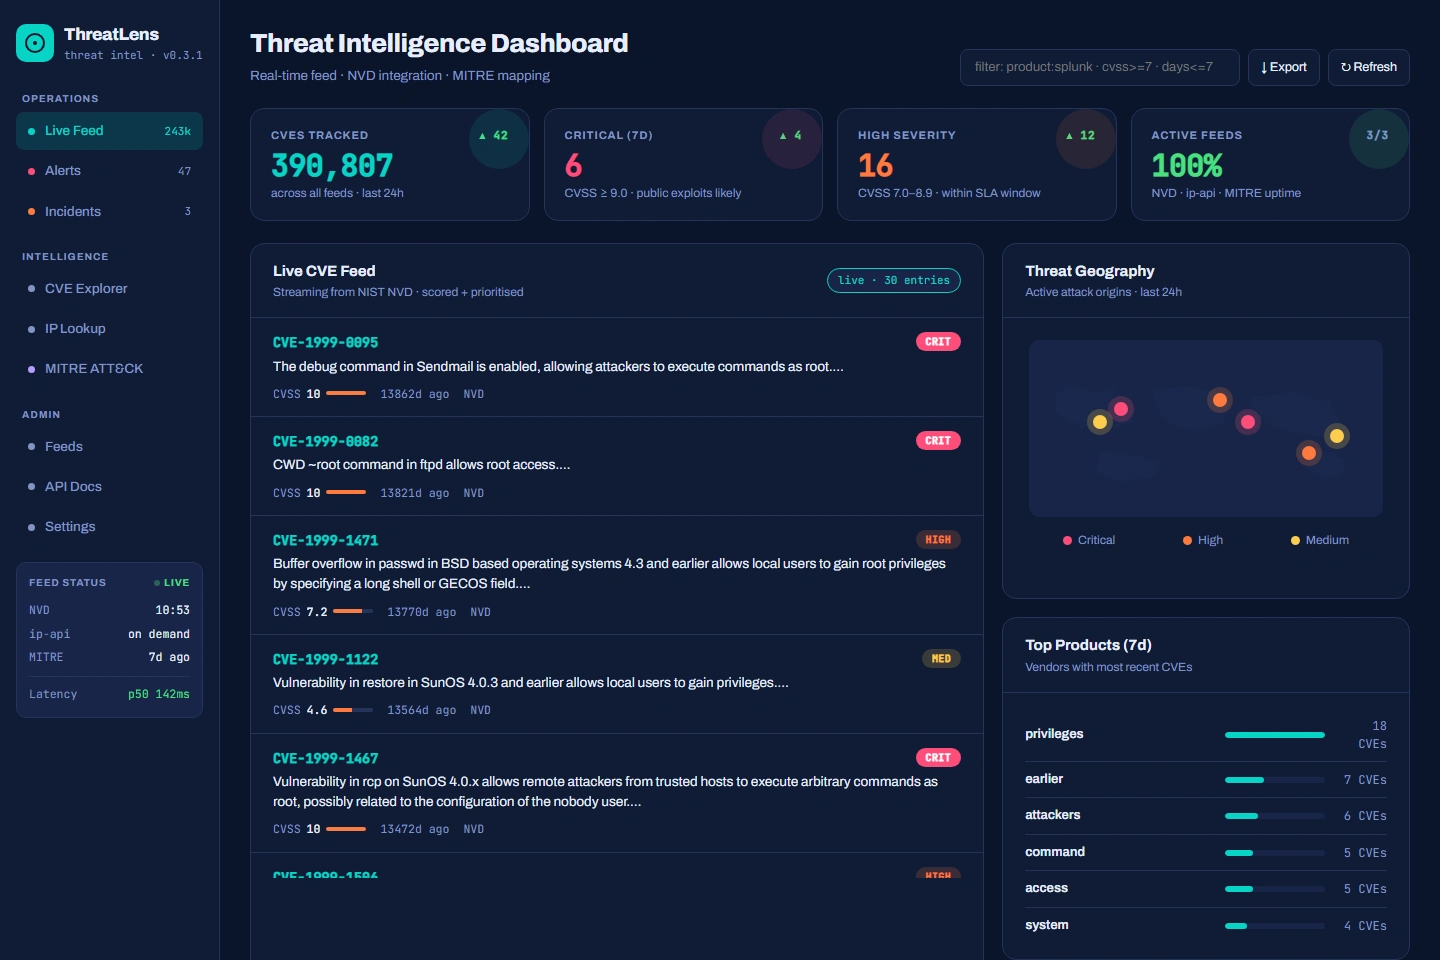
A CVE triage service that pre-ranks vulnerabilities by what is actually exploitable against your assets.
The challenge.
Thousands of CVEs are published every month. Teams without a triage system patch alphabetically, or not at all, and waste effort on vulnerabilities nobody can reach.
The approach.
A FastAPI service that correlates NVD CVE data with exploit availability, asset exposure and MITRE ATT&CK techniques, producing one composite risk score per vulnerability.
Engineering decisions.
-
Pulls and normalises live CVE data from the NVD API.
-
Composite score blends exploit availability, asset exposure and mapped ATT&CK techniques.
-
Typed request and response models with Pydantic for a clean, documented API.
The outcome.
A pre-ranked patch queue. The vulnerabilities that are actually exploitable against assets you actually run rise to the top, so triage time goes to the things that matter.